After the lead auditor asks, “Can you show me the change history on this document?” approximately ninety seconds into an audit, a quality team experiences a specific kind of silence. Nobody knows the answer, therefore the room doesn’t go silent. Everyone stops talking, thus it becomes quiet.
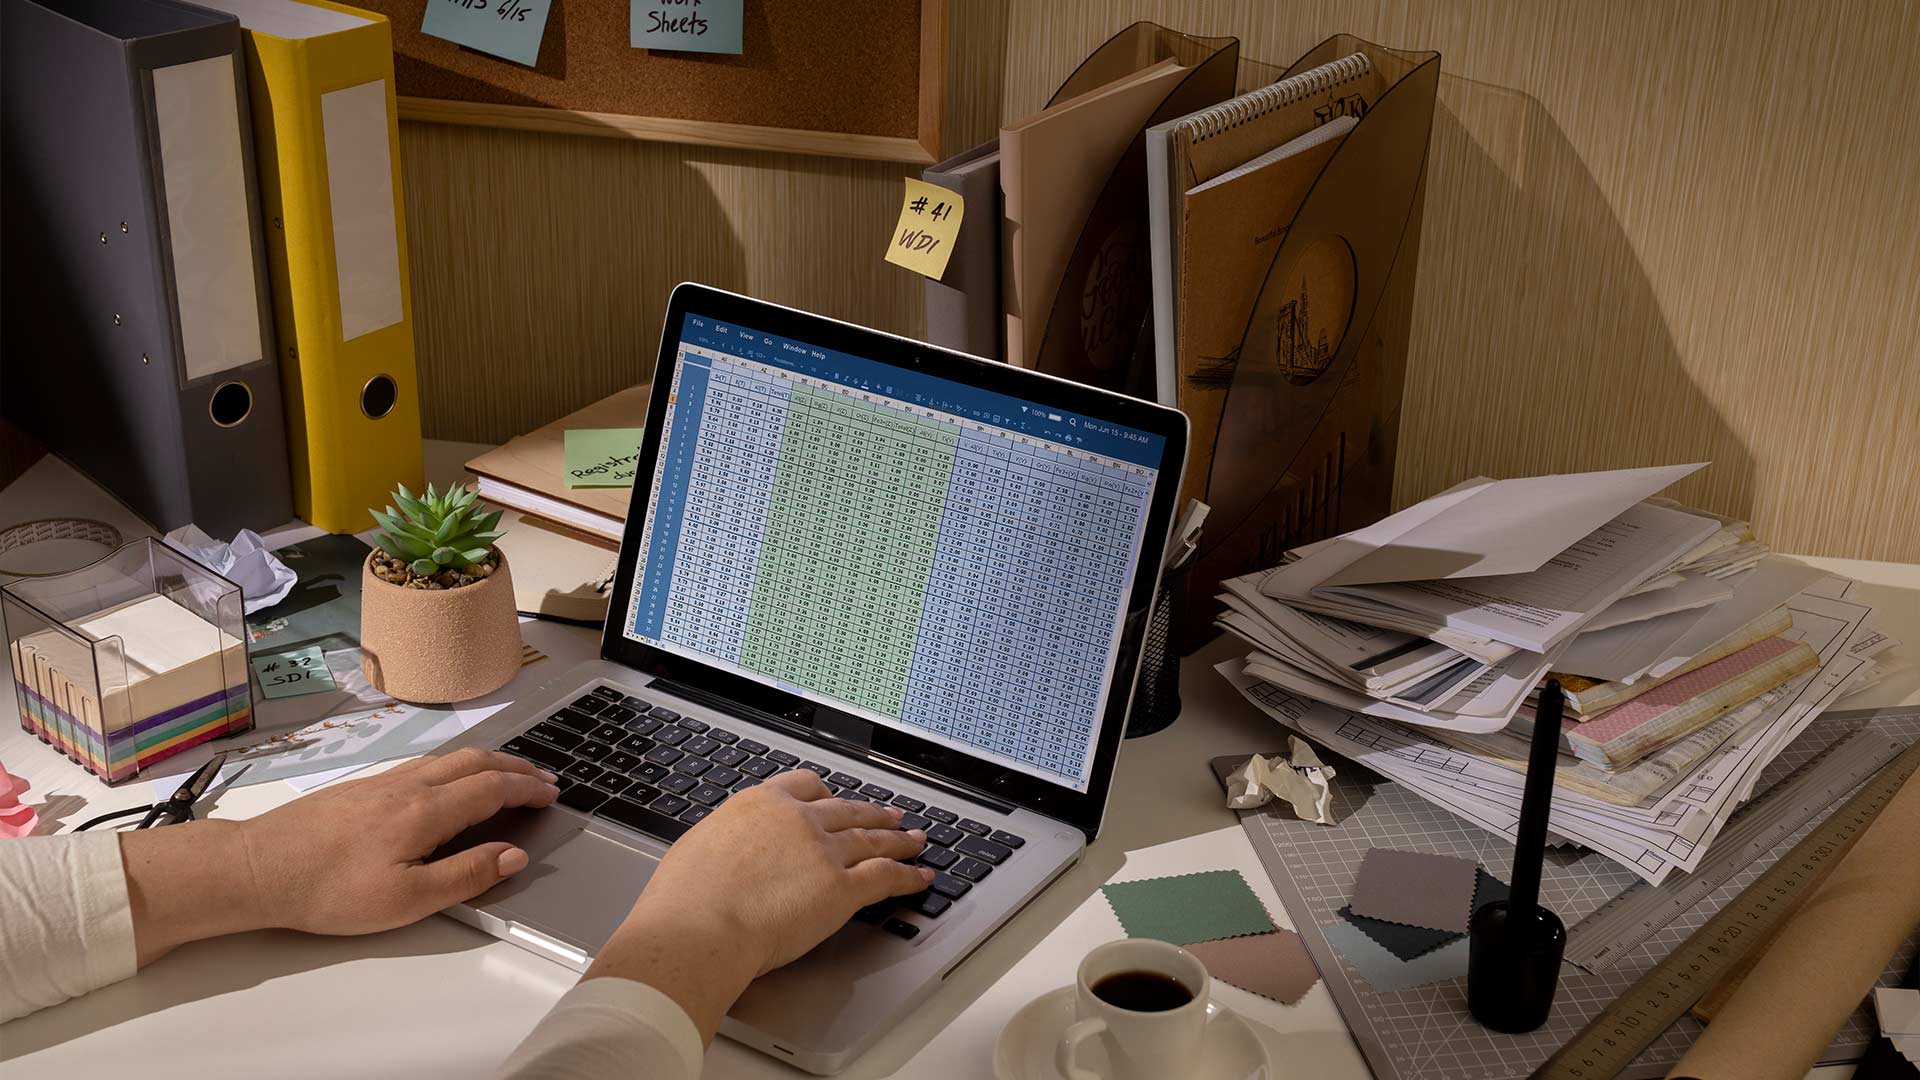
The shared drive is opened by someone. The folder is named “CAPA Tracker.” It contains CAPA_Tracker_FINAL.xlsx, CAPA_Tracker_FINAL_v2.xlsx, CAPA_Tracker_FINAL_v2_Jan_USE_THIS_ONE.xlsx, and an additional file that was edited eleven minutes ago by a person who is currently on a plane. Which version accurately captures reality is a mystery. No one knows for sure who altered cell M47 last Tuesday, why, or if anyone evaluated the modification before it became the official record. The auditor isn’t being difficult. They’re asking the single most reasonable question in quality management, and the spreadsheet — by its nature, not by anyone’s negligence — cannot answer it.
If that scene feels uncomfortably specific, it should. It plays out in conference rooms across pharmaceutical plants, medical device shops, food manufacturers, and commercial labs with a regularity that should trouble an entire industry more than it apparently does. Quality teams keep building their compliance infrastructure on a tool that was designed, with admirable success, to do something else entirely: perform calculations on numbers. Spreadsheets are exceptional at that. They are structurally, fundamentally unsuited to being a system of record for a regulated quality management system, and the gap between what they’re asked to do and what they’re built to do shows up exactly when it matters least — under audit, under investigation, under pressure.
The Document That Has Eleven Identities
Version control is the failure mode everyone recognizes first because it’s the one that announces itself loudly. A controlled document under ISO 9001 or 21 CFR Part 11 needs exactly one current, authoritative version, accessible to the people who need it, with everyone else’s copy clearly marked obsolete or removed from circulation. Spreadsheets resist this requirement at a structural level. Every email attachment is a new copy. Every “Save As” creates a fork. Every well-meaning team member who downloads a file to “just check something” introduces the possibility that their local edit becomes, through some chain of forwarded emails and good intentions, the version someone else relies on six weeks later.
This isn’t a training problem. It isn’t solved by asking people to be more careful with filenames, though that’s usually the first instinct — and the reason audit findings so often cite the same root cause dressed up in different language. The problem is architectural. A spreadsheet file has no concept of “the one true version currently in effect.” It only knows the file in front of you, right now, on your machine. Multiply that across a document library spanning SOPs, work instructions, forms, and specifications, replicated across however many people touch them, and you get a quality system where the canonical record is, in practice, whatever copy the person answering the auditor’s question happens to have open.
Building an Audit Trail Out of Memory and Goodwill
The second failure runs deeper, because it’s invisible until the exact moment someone needs it. An audit trail isn’t a nice-to-have feature bolted onto good recordkeeping — it’s the evidentiary backbone that lets an organization demonstrate, after the fact, that a record changed the way it should have, by the people authorized to change it, for documented reasons. Clauses covering nonconforming outputs and corrective action under ISO 9001, and the electronic recordkeeping expectations under 21 CFR Part 11, all rest on the same premise: that the history of a record is itself a record.
Spreadsheets weren’t built to keep that history. They were built to let you type a number into a cell and overwrite whatever number was there before, instantly and irreversibly, with no native log of the change, the timestamp, the previous value, or the person who made it. You can bolt on a “last modified by” column. You can ask your team to leave a comment whenever they edit something significant. People will do this diligently for a while. Then a deadline arrives, a row gets deleted to “clean things up,” a tab gets overwritten with last quarter’s template, and the chain of custody that auditors are specifically trained to look for simply isn’t there to find. Reconstructing it afterward — through old email attachments, calendar invites, and someone’s recollection of a Tuesday three months ago — is not an audit trail. It’s an archaeology project, undertaken under deadline, with regulatory consequences riding on its accuracy.
CAPA, Running on Inboxes
Nowhere does the spreadsheet model strain harder than in CAPA management, and nowhere are the stakes higher. A corrective and preventive action isn’t a single event — it’s a lifecycle. Containment, root cause investigation, an action plan, implementation, effectiveness verification, closure. Each stage typically belongs to a different person, has its own deadline, and depends on visibility into what came before it.
In a spreadsheet-driven environment, that lifecycle is held together entirely by human effort. Someone opens a CAPA row, assigns an owner by typing their name into a cell, and then the actual coordination — the part where work gets routed, reminded, escalated, and verified — moves into email. The spreadsheet becomes a static ledger that someone has to remember to update, sitting alongside a parallel and uncoordinated thread of messages, attachments, and “just following up” replies that constitute the real working record of what happened. When that person goes on leave, the CAPA stalls. When an inbox gets reorganized or a thread gets buried, the trail goes cold. None of this shows up as a dramatic failure in the moment. It shows up months later as a CAPA that’s open well past its target closure date, with no clean record of why, presented to an auditor who has seen this exact pattern in a hundred other companies and knows precisely what it indicates: a system run on individual effort rather than structured process. A spreadsheet doesn’t escalate an overdue action. It doesn’t route a record to the next reviewer. It doesn’t know an action is overdue at all unless a person remembers to look.
The Quiet Cost of Untraceable Change
Underneath all of this sits a more fundamental issue: traceability, the thread that should let anyone reconstruct what happened to a record across its entire life. A robust quality record doesn’t just hold today’s value. It holds the sequence of values that came before it, the reasons each one changed, and the approvals that made each change legitimate. That sequence is what lets a quality team answer the questions that actually matter during an investigation — not just “what is the current spec,” but “when did the spec change, who approved it, and what did we know at the time.”
Spreadsheets collapse that sequence by default. Overwrite a cell and the previous value is gone, full stop, unless someone happened to be diligent enough to preserve it elsewhere — in a separate “change log” tab that itself depends entirely on people remembering to fill it in correctly, every time, with no enforcement mechanism if they don’t. The cost of this isn’t abstract. A 2017 Ponemon Institute study, conducted with Globalscape, put the average total cost of non-compliance for an organization at roughly $14.8 million — and untraceable change is precisely the kind of gap that turns a routine audit finding into a non-compliance event with that price tag attached. The investigation doesn’t fail because the team lacked diligence. It fails because the tool they were diligent in never had a mechanism for preserving what they did.
What a Real Quality Management System Actually Changes
A purpose-built QMS doesn’t approach these problems as features to add. It approaches them as the foundation the system is built on, which is the actual distinction worth understanding — not “more functionality,” but a different relationship between the system and the data it holds.
Document control stops being a matter of trust and becomes a matter of architecture. There is one current version of a controlled document, enforced by the system rather than requested of the team, with prior versions retained, dated, and clearly marked obsolete rather than floating around in inboxes under ambiguous filenames. Every record carries its own audit trail natively — every edit, every approval, every status change captured automatically with a timestamp and an identity attached, because the system was built to do that, not asked to remember to. CAPA stops living in two places at once. Ownership, deadlines, and escalation become structural properties of the workflow itself, so an overdue action surfaces on its own rather than waiting for someone to notice an email went unanswered. And change, instead of erasing what came before it, becomes additive — each revision sitting on top of the last, fully reconstructable, because traceability is what the system is for rather than a habit the team is hoping to maintain under pressure.
This isn’t a theoretical upgrade. With the QMSR now in force — the FDA’s harmonization of 21 CFR Part 820 with ISO 13485:2016, effective February 2, 2026 — device manufacturers are now operating under a regulation that gives FDA investigators explicit authority to review management review records, internal audit reports, and supplier audit documentation that were previously shielded from inspection. The margin for “we’ll reconstruct it from email if they ask” has narrowed considerably, at precisely the moment the volume of inspectable records expanded.
Sound Familiar?
If you’ve spent any part of the last audit cycle hunting for the “real” version of a document, explaining a CAPA delay you can’t fully account for, or trying to remember whether a number changed because someone caught an error or someone fat-fingered a cell — you already know spreadsheets aren’t a quality management system. They’re a workaround that’s been asked to carry more weight than they were ever designed to hold, and the strain shows up exactly where you can least afford it: in front of an auditor, in the middle of an investigation, in the gap between what you can prove and what you know to be true.
QISS QMS was built around the part of this problem that spreadsheets can’t solve no matter how carefully your team manages them. Document control with a single enforced current version. CAPA workflows that route, escalate, and verify on their own instead of waiting on someone’s inbox. A native audit trail on every record, not a column someone has to remember to fill in. It’s the structural difference between a quality system you maintain through individual vigilance and one that maintains itself — which, when an auditor is sitting across the table, is the only kind worth having.
See how QISS QMS replaces the spreadsheet chaos with a system built for compliance →
Related Articles:
- How to Design a Laboratory Compliance Framework from Scratch
- Document and Record Control in ISO-Compliant Labs: Where LIMS Fits In
- QISS QMS Audit Management vs. Spreadsheet-Based Audits — Why the Switch Pays Off
- Sample Labeling and Traceability Standards in the U.S.
- FDA Requirements for Laboratory Sample Management